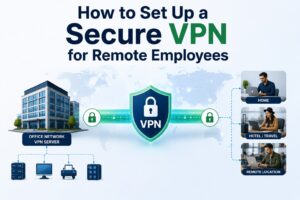
A VPN is one of the most effective ways to secure internet traffic, connect remote employees to business networks, and safely access systems from anywhere. However, VPN connections can sometimes stop working, become slow, disconnect frequently, or cause DNS and routing problems.
The good news is that many common VPN problems can be diagnosed and fixed quickly.
In this guide, I’ll explain the most common VPN issues, what causes them, and the practical steps you can take to troubleshoot them.
- VPN Is Not Connecting
One of the most common VPN problems is simply being unable to establish a connection.
You may see messages such as:
- VPN connection failed
- Unable to connect to server
- Connection timed out
- Handshake failed
- Server unreachable
Common Causes
A VPN may fail to connect because of:
- Incorrect VPN credentials
- Wrong server address or hostname
- Incorrect VPN configuration
- Blocked VPN ports
- Firewall or NAT restrictions
- ISP restrictions
- Incorrect system time
- VPN server being offline
- Invalid certificates or keys
How to Fix It
Start by checking the VPN configuration and credentials.
For WireGuard, verify that the private key, public key, endpoint, allowed IPs, and port are configured correctly.
For OpenVPN, check the server address, port, protocol, certificates, authentication settings, and client configuration file.
Also confirm that the VPN server is reachable from the internet and that the required port is forwarded correctly through the router or firewall.
If the VPN is behind NAT, make sure port forwarding and firewall rules allow the required traffic.
- VPN Is Connected but There Is No Internet Access
Sometimes the VPN appears to connect successfully, but websites do not load.
This usually indicates a routing, DNS, firewall, or NAT problem.
Possible Causes
- Incorrect default route
- Full-tunnel VPN misconfiguration
- DNS server unreachable
- Firewall blocking forwarded traffic
- NAT/masquerading not configured
- Incorrect AllowedIPs configuration
- Split-tunnel configuration problems
How to Fix It
First, determine whether the problem affects all traffic or only certain destinations.
Try accessing an IP address directly rather than a domain name. For example, if an IP works but a website name does not, you may have a DNS problem.
For a full-tunnel VPN, verify that traffic is being routed through the VPN server and that the VPN server is performing NAT correctly.
With WireGuard, pay particular attention to the AllowedIPs setting. A configuration such as:
0.0.0.0/0
typically routes IPv4 traffic through the VPN tunnel.
Incorrect routing rules can cause internet access to stop completely.
- VPN Connection Is Very Slow
A VPN can significantly improve security, but encryption and network routing can add some overhead.
If your VPN speed is much lower than your normal internet speed, troubleshooting is necessary.
Common Reasons for Slow VPN Speed
- VPN server is overloaded
- Server is geographically far away
- Weak Wi-Fi connection
- High CPU usage on the router
- Poor encryption performance
- Incorrect MTU
- ISP routing issues
- Double NAT
- Limited travel-router hardware
- VPN protocol overhead
How to Fix a Slow VPN
Start by testing the internet connection without the VPN.
Then compare it with the VPN connection.
This helps identify whether the problem is your ISP connection or the VPN itself.
You should also test different VPN server locations. A server that is physically closer to the user often provides better latency and performance.
For router-based VPNs, check CPU and memory utilization. Some lower-powered routers may struggle with high-speed encryption.
Check MTU
Incorrect MTU settings can cause fragmentation and poor performance.
A properly configured MTU can improve stability and speed, particularly when using VPN connections over networks with additional encapsulation.
For advanced troubleshooting, test packet sizes and gradually adjust the MTU rather than simply choosing a random value.
- VPN Keeps Disconnecting
Frequent VPN disconnections can be extremely frustrating, especially for remote workers who need continuous access to business resources.
Common Causes
- Unstable internet connection
- Wi-Fi interference
- VPN server timeout
- NAT timeout
- Firewall behavior
- Keepalive settings
- Router firmware issues
- ISP instability
- Network switching between Wi-Fi and mobile data
WireGuard Troubleshooting
For WireGuard, the PersistentKeepalive option can help maintain connectivity when a client is behind NAT or a restrictive firewall.
A common value is:
PersistentKeepalive = 25
This is particularly useful for devices that need to maintain a connection through NAT.
However, keepalive should be used where appropriate rather than added blindly to every configuration.
Additional Steps
Check the VPN logs and determine exactly when the connection drops.
If the connection always fails after a similar amount of time, investigate NAT or firewall session timeouts.
- VPN Is Connected but Some Websites or Applications Do Not Work
This is another common VPN troubleshooting scenario.
The VPN may be working correctly for some traffic while specific websites, services, or applications fail.
Possible Causes
- DNS problems
- Incorrect routing
- Split tunneling
- IPv6 routing issues
- Firewall restrictions
- Application-specific network requirements
- Geo-blocking
- MTU problems
What to Check
Test the affected service both with and without the VPN.
Then check:
- DNS resolution
- IPv4 connectivity
- IPv6 connectivity
- Routing table
- Firewall rules
- VPN AllowedIPs or route configuration
In business environments, make sure internal routes are advertised or manually configured so users can reach private subnets through the VPN.
- DNS Leaks or DNS Resolution Problems
A VPN should route DNS traffic appropriately when privacy or secure remote access is required.
A DNS leak can occur when your device sends DNS requests outside the VPN tunnel.
This may expose DNS queries to the local ISP or another DNS provider.
Common DNS Problems
- Websites do not resolve
- Internal company domains cannot be accessed
- DNS requests bypass the VPN
- DNS server is unreachable
- Incorrect DNS configuration
- DNS rebind protection or firewall restrictions
How to Fix DNS Issues
Check which DNS servers the client is using while connected to the VPN.
For a business VPN, internal DNS servers may be required to resolve internal hostnames.
For remote-access VPNs, make sure DNS requests are routed through the intended VPN interface.
After making changes, test DNS resolution again.
You can use commands such as:
nslookup example.com
or:
nslookup internal-server.company.local
This can help determine whether the issue is DNS-related or caused by routing.
- VPN Works on Wi-Fi but Not on Mobile Data
A VPN that works perfectly on one network may fail on another.
This is especially common with mobile networks, public Wi-Fi, hotel networks, and corporate networks.
Why This Happens
Different networks may use:
- Carrier-grade NAT
- Aggressive firewall filtering
- Restricted UDP traffic
- Captive portals
- Blocked VPN ports
- Different MTU values
If WireGuard does not work on one network but works on another, test whether the network is filtering or blocking UDP traffic.
For OpenVPN, TCP-based configurations can sometimes work in environments where UDP connectivity is restricted, although TCP-over-TCP can introduce performance drawbacks.
- VPN Authentication Keeps Failing
Authentication problems are common in business VPN environments.
You may see errors related to:
- Invalid username or password
- Expired certificate
- Incorrect pre-shared key
- Invalid private key
- MFA failure
- Account lockout
- Authentication server unavailable
Troubleshooting Steps
Verify the user’s credentials first.
Then check whether the account is active and permitted to use the VPN.
For certificate-based VPNs, confirm that certificates are valid and have not expired.
For WireGuard, carefully verify the client and server key pairs. A single incorrect key can prevent the tunnel from establishing.
- VPN Handshake Is Failing
A VPN handshake failure usually indicates that the client and server cannot successfully establish the encrypted tunnel.
This is particularly important when troubleshooting WireGuard.
Check the Following
- Server public key
- Client private key
- Endpoint address
- UDP port
- Firewall rules
- NAT/port forwarding
- AllowedIPs
- System time
- Server availability
For WireGuard, the handshake status can provide valuable information.
If there has never been a successful handshake, start by checking connectivity and firewall rules.
If the handshake works but traffic does not pass, focus on routing, AllowedIPs, firewall, and NAT configuration.
- Remote Users Cannot Access Internal Office Resources
A VPN can show as connected while users still cannot access internal systems.
For example, the user may connect to the VPN but be unable to reach:
- File servers
- NAS devices
- Printers
- RDP servers
- Internal websites
- VoIP systems
- Network management interfaces
Common Causes
This is often a routing problem.
The VPN client needs a route to the internal network, and the VPN server must know how to reach the client’s VPN subnet.
For example:
Office Network: 192.168.10.0/24
VPN Network: 10.10.10.0/24
Both networks need appropriate routing and firewall policies.
The office network may also need a route back to the VPN client subnet.
This is one of the most frequently overlooked issues in secure remote access VPN deployments.
A Simple VPN Troubleshooting Process
When troubleshooting a VPN, I recommend using a structured approach instead of changing multiple settings at once.
Step 1: Test the Internet Connection
Confirm that the device has normal internet access before connecting to the VPN.
Step 2: Test the VPN Connection
Determine whether the VPN connects at all.
Step 3: Check the Logs
VPN logs often provide the fastest clue about what is wrong.
Look for:
- Authentication errors
- Handshake failures
- Timeout messages
- DNS errors
- Connection resets
- Certificate errors
Step 4: Check Routing
Verify that traffic is going through the correct interface.
On Windows, you can use:
route print
On Linux:
ip route
Step 5: Test DNS
Use:
nslookup example.com
Determine whether DNS works through the intended VPN path.
Step 6: Test Connectivity
Use tools such as:
ping
tracert
traceroute
For more advanced troubleshooting, iperf3 can help measure throughput and identify performance problems.
Step 7: Check Firewall and NAT
Make sure the VPN server, router, and firewall are allowing the necessary traffic.
Step 8: Change One Setting at a Time
Avoid changing multiple VPN settings simultaneously.
Make one change, test the connection, and document the result.
This makes troubleshooting much faster and prevents creating additional problems.
WireGuard vs. OpenVPN Troubleshooting
Both WireGuard and OpenVPN are widely used VPN technologies, but troubleshooting them can be slightly different.
WireGuard
When troubleshooting WireGuard, focus on:
- Key pairs
- Endpoint configuration
- UDP connectivity
- AllowedIPs
- Handshake status
- PersistentKeepalive
- Routing
- Firewall/NAT
WireGuard is lightweight and generally simple to configure, but incorrect routing or key configuration can stop traffic from passing even when the interface appears active.
OpenVPN
For OpenVPN, check:
- Certificates
- Username/password
- Server address
- Port
- TCP/UDP protocol
- Encryption settings
- Authentication
- Routing
- Firewall rules
OpenVPN logs are particularly useful because they often provide detailed information about authentication and connection failures.
When Should You Contact a VPN Professional?
Some VPN problems can be fixed in a few minutes, while others require deeper network analysis.
Professional assistance may be useful when:
- A site-to-site VPN is not working
- Multiple offices need secure connectivity
- Remote users cannot access internal systems
- VPN performance is consistently poor
- Firewall rules are complex
- Double NAT or CGNAT is involved
- WireGuard or OpenVPN configuration is unstable
- A business needs a secure remote-access solution
- You need router-based VPN deployment
- VPN monitoring and maintenance are required
A proper troubleshooting process can save hours of trial and error.
Need Help With VPN Troubleshooting?
I provide VPN troubleshooting and secure remote access services for home users, remote workers, and small businesses.
I can help troubleshoot and configure:
- WireGuard VPN
- OpenVPN
- IPsec VPN
- Site-to-site VPN
- Remote-access VPN
- Travel router VPN
- Router-based VPN
- Firewall and NAT
- DNS and routing
- VPN performance
- VPN connection stability
- Secure remote network access
Whether your VPN is not connecting, running slowly, disconnecting, or failing to provide access to internal resources, I can help identify the underlying network problem and implement a reliable solution.
Need help with your VPN? Visit Ahmad Networks to learn more about my networking and VPN services.
Frequently Asked Questions
Why is my VPN not connecting?
A VPN may fail to connect because of incorrect credentials, configuration errors, blocked ports, firewall restrictions, NAT issues, an unavailable VPN server, or incorrect encryption or certificate settings.
Why is my VPN so slow?
Slow VPN performance can be caused by server location, network congestion, weak Wi-Fi, router CPU limitations, MTU issues, ISP routing, or VPN protocol overhead.
Why does my VPN keep disconnecting?
Frequent VPN disconnections are often caused by unstable internet connectivity, NAT timeouts, firewall restrictions, Wi-Fi problems, or incorrect keepalive settings.
How do I troubleshoot a WireGuard VPN?
Check the client and server keys, endpoint, UDP port, AllowedIPs, handshake status, firewall rules, routing, NAT, and PersistentKeepalive settings.
How do I check for a DNS leak?
Check the DNS servers being used while connected to the VPN and verify that DNS requests are being routed through the intended VPN connection.
Can a VPN work behind CGNAT?
Yes, depending on the VPN architecture and connectivity requirements. However, CGNAT can make inbound connections more difficult and may require a public server, relay, or an alternative VPN architecture.
Final Thoughts
Most common VPN problems are caused by a relatively small number of issues: connectivity, routing, DNS, firewall rules, NAT, authentication, or configuration errors.
The key is to troubleshoot systematically.
Instead of repeatedly changing VPN settings, start with basic connectivity, check logs, verify routing and DNS, and then examine firewall and NAT behavior.
For businesses and remote workers, a properly configured VPN provides secure and reliable access without unnecessary complexity.
Ahmad Networks provides professional VPN troubleshooting, network configuration, and secure remote access solutions.